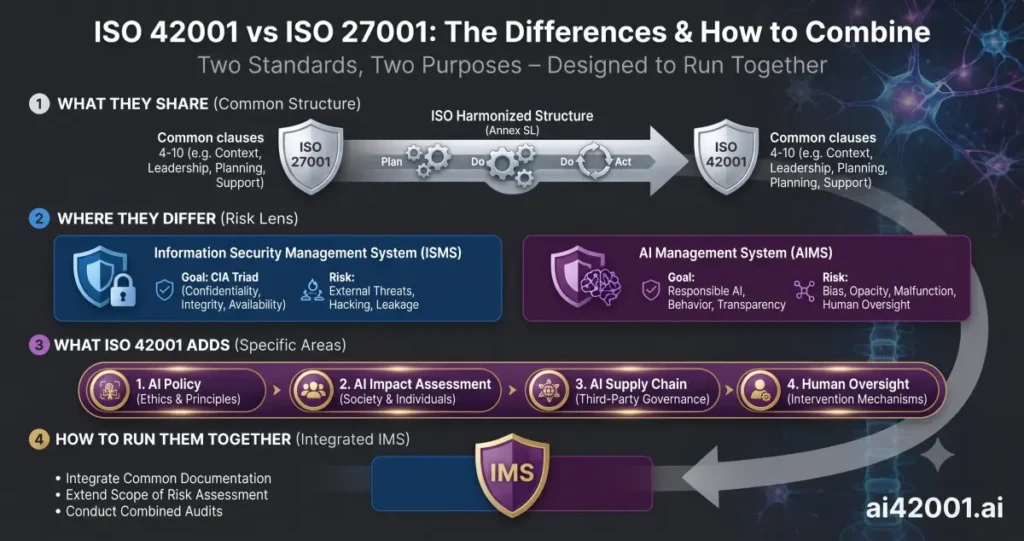
Comparison of ISO 42001 and ISO 27001 in four parts: what they share — common Clauses 4-10 under the ISO harmonized structure (Annex SL), shown as a Plan-Do-Check-Act flow between the two standards; where they differ — ISO 27001 as an ISMS aimed at the CIA triad against external threats, ISO 42001 as an AIMS aimed at responsible AI against bias, opacity, malfunction, and human-oversight risks; what ISO 42001 adds — AI policy, AI impact assessment, AI supply chain, and human oversight; and how to run them together as one integrated management system through shared documentation, extended risk assessment, and combined audits.

ISO 42001 vs ISO 27001: the differences, and how to run them together

Two different standards, two different purposes — and they are designed to run together As organizations adopt AI faster, one question comes up again and again: “We’re already certified to ISO 27001 — do we also need ISO 42001?” The short answer: they are two different standards with two different purposes, and they are designed

ISO 42001 vs ISO 27001: the differences, and how to run them together Read More »